Alex Morgan
AI Security Researcher at DeepWall
Alex Morgan is an AI Security Researcher at DeepWall, working on how attackers target and abuse AI systems.
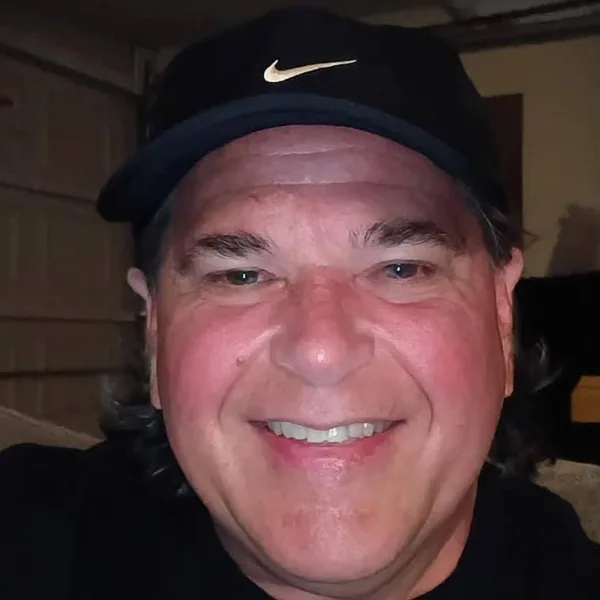
Alex Morgan · AI Security Researcher · DeepWall
Alex Morgan, AI Security Researcher at DeepWall
Alex Morgan is an AI Security Researcher at DeepWall. Alex has been in cybersecurity since 2014, working across network defense, threat intelligence, incident response and cloud security architecture, and now focuses on how attackers target and abuse AI systems.
I started my career defending enterprise networks as a Network Security Engineer at Cisco Systems. There I managed Cisco Secure Firewall (ASA/Firepower) and Identity Services Engine (ISE) deployments, mitigated Layer 3–7 attacks and ran vulnerability assessments and compliance audits.
From there I moved into threat intelligence at Mandiant (now Google Cloud). I tracked and profiled advanced persistent threat (APT) groups and turned technical indicators into intelligence briefings for critical-infrastructure stakeholders and government defense contractors. Working with red teams to simulate real adversary tactics taught me to think about security from the attacker's side.
At CrowdStrike I led incident response investigations into ransomware and nation-state attacks. I used the Falcon platform for endpoint forensics, malware analysis and threat hunting, and wrote custom remediation scripts to get clients back on their feet faster. As Lead Cloud Security Architect at Palo Alto Networks, I designed zero-trust cloud security architectures on Prisma Cloud for Fortune 500 clients, led a team of six engineers automating vulnerability-scanning pipelines, and worked on bringing AI-driven threat detection into cloud infrastructure.
At DeepWall I research how large language models hold up against prompt injection, data poisoning and adversarial extraction attacks. I build automated benchmarking tools to stress-test enterprise AI models and work with engineering teams on real-time guardrails for AI-driven applications. When I review an article, I'm asking one thing: would this hold up in a real investigation?
Areas of expertise
- AI security and AI-driven threats (Foundation for deepfake and synthetic-media risk content)
LLM security research on prompt injection, data poisoning and adversarial extraction; automated benchmarking of enterprise AI models; real-time AI guardrails (DeepWall)
- Adversarial attacks on AI and detection systems
Adversarial extraction and data-poisoning research (DeepWall); AI-driven threat-detection integration (Palo Alto Networks)
- Digital identity protection
Zero Trust architecture (Palo Alto Networks); Cisco Identity Services Engine (ISE) deployments (Cisco)
- Threat intelligence and impersonation or fraud campaigns (Context for brand protection)
APT tracking and profiling, adversary TTPs, executive threat briefings (Mandiant)
- Incident response and forensics
Ransomware and nation-state IR, endpoint forensics, malware analysis, threat hunting (CrowdStrike)
- Cloud and network security
Prisma Cloud zero-trust architecture, vulnerability management automation (Palo Alto Networks); firewall and network defense (Cisco)
Experience
- DeepWall (San Francisco, CA): AI Security Researcher, June 2026 – Present
- Palo Alto Networks (Santa Clara, CA): Lead Cloud Security Architect, June 2023 – June 2026
- CrowdStrike (Austin, TX): Senior Incident Response Consultant, March 2020 – June 2023
- Mandiant (now Google Cloud) (Milpitas, CA): Senior Cyber Threat Intelligence Analyst, January 2017 – March 2020
- Cisco Systems (San Jose, CA): Network Security Engineer, June 2014 – January 2017
Education and credentials
- M.S. Cybersecurity, Georgia Institute of Technology, Atlanta, GA, May 2013
- B.S. Computer Science, Stanford University, Stanford, CA, September 2011
Platforms used in practice
- Prisma Cloud
- CrowdStrike Falcon
- Cisco Secure Firewall (ASA/Firepower)
- Cisco ISE